Wednesday, November 14, 2012

Further evidence on the draft CDB

The House of Commons and House of Lords Joint Select Committee written evidence on the draft Communications Data Bill has now been updated to include submissions previously erroneously omitted, (including my own which now appears on pages 135 to 139 (origninally 580 to 584)* of the published evidence).

Additionally the (currently uncorrected) transcripts of the oral evidence of Keir Starmer, Duncan Campbell, Henry Porter and Caspar Bowden, Gus Husein and the Home Secretary, Theresa May, are now available.

Caspar Bowden's evidence, in particular, is essential reading.

* Now updated again and re-arranged in alphabetical order.

Tuesday, November 13, 2012

The MP, the outrage mob and Abu Qatada

A jury has decided that ex-MP Margaret Moran had committed 15 counts of false accounting and six counts of using a false instrument in relation to parliamentary expenses.

Interestingly, since the judge, defence and prosecution agreed that she was unfit to stand trial for mental health reasons, she can't be found guilty and sentenced to jail time.

No doubt a self-selecting proportion of the moral outrage mob, some of whom are currently in full flow over the release of Abu Qatada following the Special Immigration Appeals Commission (SIAC) decision yesterday that he can't be deported to Jordan, will say the Court is being soft on Ms Moran. There'll be accusations of faked illness and soft judges but this is probably more an example of the criminal justice system behaving appropriately and proportionately to the circumstances being assessed.

It's just a pity that the large numbers of people with mental health problems who have been sent to jail did not and do not get the consideration and treatment they need. As the Prison Reform Trust says, offering mental health and social care instead of custody would relieve pressure on prisons and could cut re offending rates.

The mob find it even harder to deal with the Abu Qatada case. WHY can't we GET RID OF the BAD MAN?!!!  Pick your choice of fall guys - the government, the judges, the courts, the EUROPEAN COURT, the HUMAN RIGHTS ACT, WHADABOUT MY HUMAN RIGHTS, the soft liberals, the list goes on. Someone on the radio this morning yelled he didn't care if Qatada got tortured - he deserved it.

Abu Qatada is on record as preaching hatred, supporting and inciting violence and has been alleged to have been directly involved in acts of terrorism. There are plenty of laws on the statute books in the UK that would enable him to be prosecuted and, most likely, convicted. The government chose instead to start the process of deporting him. It's taken years and he's still here, albeit he's spent most of that time in prison.

What are the latest reasons he cannot be sent away? The SIAC determined there were 2 key questions relating to whether evidence against Qatada obtained by torture would be used in his trial in Jordan.
"54.
The answers to two critical questions will determine whether there is a real risk that the impugned statements will be admitted probatively:
i)
Irrespective of the means by which they were obtained, are the impugned statements now admissible at all under Article 148.2 of the Code of Criminal Practice?
ii)
If they are, is there a real risk that they will be admitted even though there is a “real risk” that they have been obtained by torture? "
The angry mob really need to understand the Commission was not looking at whether Qatada was a bad guy but at whether Jordan would give him a fair trial, including avoiding the use of evidence obtained by torture.

The Commission take a look at the way the Jordanian justice system works, differing opinions on what might be allowable within the rules of the system, and whether the statements probably obtained by torture could be used in his trial (para 55 -  63).  They decide that none of the opposing professional opinions on whether the torture evidence statements could be used is definitive. The undeniable conclusion therefore must be that there is a real risk such statements could be admissible as evidence against Abu Qatada at his trial in Jordan:
"66.
Unless and until the Court of Cassation gives an authoritative ruling on the question, it must remain open. Both views are tenable... It is simply impossible for us to resolve these differences. Confronted with two tenable views of what Jordanian law provides, all that we can do is to return to the basic Strasbourg test: has the Secretary of State established that there is not a real risk that the impugned statements will be admitted probatively? To that question there can be only one answer: unless we can be confident that the court would not admit the impugned statements because they were tainted by the “real risk” of torture, the answer must be negative.
The Commission then goes on to look at whether alleged torture induced statements would be used in evidence, given there is a risk they could be admitted. They conclude that, even though Jordan's constitution was amended in 2011 to prohibit torture, people claiming they were tortured will still have the burden of proving that.
"72...It is likely to require a definitive ruling by the Court of Cassation or the newly established Constitutional Court... and place the burden of proof that the statements were not obtained by torture on the state prosecutor.
73. If the burden of proving that the impugned statements were obtained by torture is imposed on the appellant, it will be difficult to discharge. They were made over fourteen years and nearly twelve years ago respectively... The only means of eliminating a real risk that statements which may well have been obtained by torture will be admitted probatively at the appellant’s retrial would be for the burden of proving, to a high standard, that they were not, to be placed upon the prosecutor. Anything less gives rise to a real risk that they will be."
 They then conclude there remains a risk that Qatada will not get a fair trial in Jordan.
"Conclusion on the Article 6 issue
78.
The Secretary of State has not satisfied us that, on a retrial, there is no real risk that the impugned statements of Abu Hawsher and Al-Hamasher would be admitted probatively against the appellant. Until and unless a change is made to the Code of Criminal Procedure and/or authoritative rulings are made by the Court of Cassation or Constitutional Court which establish that statements made to a public prosecutor by accomplices who are no longer subject to criminal proceedings cannot be admitted probatively against a returning fugitive and/or that it is for the prosecutor to prove to a high standard that the statements were not procured by torture, that real risk will remain.
In spite of the angry radio phone-in caller's hopes that he will be tortured, the Commission also agree with the European Court of Human Rights (para 194 - 196) that there is little risk that Qatada will be tortured in Jordan, by agents of the state.
"Article 3
79.
In the light of our conclusions on the Article 6 issue, we can deal with the Article 3 issue more briefly than would otherwise have been required. SIAC has had to consider the history and circumstances of Jordan and the reliability of the assurances given by it to the United Kingdom in two judgments, handed down respectively on 26th February 2007 and 2nd November 2007 – Othman and VV. In both, SIAC concluded that the United Kingdom could safely accept solemn assurances given by the Jordanian state; and that those assurances removed the real risk that either appellant would suffer inhuman or degrading treatment at the hands of state agents in Jordan, for two fundamental reasons: the close and friendly relations which have existed at all levels in the governments of both countries for many decades; and the general coincidence of interests of the two countries in those aspects of international affairs which affect them both. The Strasbourg Court came to the same view for essentially the same reasons...
87.
We remain convinced that the government of Jordan can and will fulfil its assurances about the treatment of the appellant on return...Like the Strasbourg Court, we remain satisfied that those assurances provide, in their practical application, a sufficient guarantee that the appellant will be protected against the risk of ill-treatment by or at the behest of Jordanian state agents."
So, to summarise, we don't think he'll be tortured over there but his re-trial may be tainted by evidence obtained by torture. Where does this leave us?

Abu Qatada can smile on his release and the outrage mob can foam at their collective mouths and infer his evil satisfaction, but Ben Franklin was smarter than both them and me, and he reckoned "that it is better 100 guilty persons should escape than that one innocent person should suffer is a maxim that has been long and generally approved."

Why don't we just stick him on a plane and send him to Jordan anyway? The Italians only had to pay €15,000 each to people they wrongly deported to Libya and the Home Secretary could be a media heroine for a day or two. And as a cost benefit analysis, €15,000 or €20k or €50k or even €100k  is a lot cheaper than keeping him in jail and/or under constant surveillance and pursuing due process to get rid of him.

Well we live in a country where the government, by and large, respects the rule of law and the notion that it should apply to everyone, including the alleged bad guys. That's a good thing.

Alternately, it is possible the Home Secretary and other members of the government, in addition to wanting to protect the reputation of the UK, may be concerned about personal sanctions they might be subjected to, in the longer term, if they were to be complicit in ordering an illegal deportation.

Whatever the motivation, it is to the credit of the UK justice system that the Special Immigration Appeals Commission could continue to address this case through rational application of the rule of law, in spite of the pressures to facilitate Abu Qatada's deportation. The government will appeal the decision, as they should do, but if this man is to be deported it needs to be done by the book. Better still, if he is as dangerous and guilty as has been alleged, bring the evidence you have against him before a UK court and put him on trial here.

Friday, November 09, 2012

Apple's telling off by UK Court of Appeal

The Rt Hon. Professor Sir (formally Lord Justice) Robin Jacob's polite lambasting of Apple last week is now available in full at Bailli, Neutral Citation Number: [2012] EWCA Civ 1430; Case No: A3/2012/1845. It's a fun read, particularly paragraphs 18 to 32 which I hope the Rt Hon judge won't mind me reproducing here in their entirety.
"         My conclusions as regards the Contested Notice
  1. Mr Michael Beloff QC for Apple submitted that Apple could not be held responsible for inaccurate reporting by journalists. But it can, if it contributed to that inaccuracy by inaccurate statements and false innuendo in the Contested Notice as I consider it did.

  2. For I accept all of Samsung's contentions. Firstly I do not consider it was open to Apple to add matter in the middle of the notice we ordered to be published. A notice with such matter is simply not the notice ordered.
  3. Even if that were not so, it cannot be legitimate to break up the ordered notice with false material. And the matter added was indeed false. Before introducing the quotes from HHJ Birss it begins:
  4. In the ruling, the judge made several important points comparing the designs of the Apple and Samsung products.
    But the Judge was not comparing "the Apple and Samsung products." There is not and has never been any Apple product in accordance with the registered design. Apple's statement would clearly be taken by ordinary readers and journalists to be a reference to a real Apple product, the iPad. By this statement Apple was fostering the false notion that the case was about the iPad. And that the Samsung product was "not as cool" as the iPad.

  5. I turn to the last paragraph. I do not think the order as made precluded any addition to the required notice if that addition had been true and did not undermine the effect of the required notice. But I do consider that adding false and misleading material was illegitimate. For by adding such material the context of the required notice is altered so that it will be understood differently.

  6. Here what Apple added was false and misleading. I turn to analyse it. The first sentence reads:
  7. However, in a case tried in Germany regarding the same patent, the court found that Samsung engaged in unfair competition by copying the iPad design.
    That is false in the following ways:
    (a) "Regarding the same patent." No patent of any kind has been involved in Germany or here, still less "the same patent."
    (b) As regards the Community Registered Design, the German Courts held that neither the Galaxy 10.1 nor the 8.9 infringed it. As to the 7.7 there was for a short while a German provisional order holding that it infringed. Whether there was a jurisdiction to make that order is very doubtful for the reasons given in my earlier judgment but in any event the order had been (or should have been) discharged by the time the Contested Notice was published.
    (c) There is a finding and injunction, limited to Germany alone, that the 10.1 and 8.9 infringe German unfair competition law. But the statement is likely to be read as of more general application.

  8. The second sentence reads:
  9. A U.S. jury also found Samsung guilty of infringing on Apple's design and utility patents, awarding over one billion U.S. dollars in damages to Apple Inc.
    That is misleading by omission. For the US jury specifically rejected Apple's claim that the US design patent corresponding to the Community Design in issue here was infringed. The average reader would think that the UK decision was at odds with that in the US. Far from that being so, it was in accordance with it.

  10. The third sentence reads:
  11. So while the U.K. court did not find Samsung guilty of infringement, other courts have recognized that in the course of creating its Galaxy tablet, Samsung wilfully copied Apple's far more popular iPad.
    This is calculated to produce huge confusion. The false innuendo is that the UK court came to a different conclusion about copying, which is not true for the UK court did not form any view about copying. There is a further false innuendo that the UK court's decision is at odds with decisions in other countries whereas that is simply not true.

  12. The reality is that wherever Apple has sued on this registered design or its counterpart, it has ultimately failed. It may or may not have other intellectual property rights which are infringed. Indeed the same may be true the other way round for in some countries Samsung are suing Apple. But none of that has got anything to do with the registered design asserted by Apple in Europe. Apple's additions to the ordered notice clearly muddied the water and the message obviously intended to be conveyed by it.

  13. Jurisdiction to make a Further Order

  14. Mr Beloff suggested that we had no jurisdiction to make a further order. But he accepted that the court has power to vary its orders to make their meaning and intention clear. The meaning and intention of the first order was plain: to require Apple to publicise properly that there was no infringement of the registered design. The proposed order now sought does no more than that.

  15. So it is unnecessary to explore further the power of the court to grant an injunction where an earlier court order has been breached or disobeyed. One would expect such a power to exist irrespective of formal proceedings for contempt. As my late father observed:
  16. Under its inherent jurisdiction, the court has undoubted power to compel observance of its process and obedience of and compliance with its orders. These powers are inherent in the sense that they are necessary attributes to render the judicial function effective in the administration of justice, The Inherent Jurisdiction Current Legal Problems, 1970 p.44
    The Form of the Further Order

  17. The form of this was settled at the hearing. So I need do no more than explain the reasons for the matters over which there was some dispute.

  18. Given our finding that the Contested Notice did not comply with our order and did not achieve what was intended there was no dispute but that we should order it be removed. There was dispute as to what should go up in its place. Apple contended that no more was needed on its home page. We thought otherwise. The Contested Notice had had over a million hits. It was necessary that the fact it was misleading be brought home. Only a notice on Apple's homepage could be sure to do that. We were of course conscious that a notice on the homepage was highly undesirable from Apple's point of view, but its own actions had made it necessary. We also thought that a rather longer period was needed than the one month period of the original order. We ordered that the notice and link should stay up until 15th December. The notice on the homepage had to make it clear that the Contested Notice was inaccurate and did not comply with the first order.

  19. We also thought it appropriate that the correct statement – the notice required by the original notice – should appear without modification or addition. Apple's previous modifications and additions made it clear that it should not be allowed to do the same or something similar again. Of course that did not preclude it from making statements elsewhere – even untrue ones which might amount to a libel or malicious falsehood. That would amount to a prior restraint which would obviously be inappropriate. All we required is that the notice we ordered should appear unvarnished or unembellished in any way.

  20. As to the costs (lawyers' fees) to be awarded against Apple, we concluded that they should be on an indemnity basis. Such a basis (which is higher than the normal, "standard" basis) can be awarded as a mark of the court's disapproval of a party's conduct, particularly in relation to its respect for an order of the court. Apple's conduct warranted such an order.

  21. Finally I should mention the time for compliance. Mr Beloff, on instructions (presumably given with the authority of Apple) told us that "for technical reasons" Apple needed fourteen days to comply. I found that very disturbing: that it was beyond the technical abilities of Apple to make the minor changes required to own website in less time beggared belief. In end we gave it 48 hours which in itself I consider generous. We said the time could be extended by an application supported by an affidavit from a senior executive explaining the reasons why more was needed. In the event no such application was made. I hope that the lack of integrity involved in this incident is entirely atypical of Apple."
I admire his inherent optimism, in spite of the evidence in this particular case, in his concluding hope that  "the lack of integrity involved in this incident is entirely atypical of Apple."

Apple have now put a link to the ordered notice on their website.  You do have to scroll down to the bottom of the http://www.apple.com/uk/ homepage to find it:
"On 25 October 2012, Apple Inc. published a statement on its UK website in relation to Samsung's Galaxy tablet computers. That statement was inaccurate and did not comply with the order of the Court of Appeal of England and Wales. The correct statement is at Samsung/Apple UK judgement."
 The notice itself now reads:
"Samsung / Apple UK judgment
On 9 July 2012 the High Court of Justice of England and Wales ruled that Samsung Electronic (UK) Limited’s Galaxy Tablet Computers, namely the Galaxy Tab 10.1, Tab 8.9 and Tab 7.7 do not infringe Apple’s Community registered design No. 0000181607-0001. A copy of the full judgment of the High Court is available from www.bailii.org/ew/cases/EWHC/Patents/2012/1882.html.
That Judgment has effect throughout the European Union and was upheld by the Court of Appeal of England and Wales on 18 October 2012. A copy of the Court of Appeal’s judgment is available from www.bailii.org/ew/cases/EWCA/Civ/2012/1339.html. There is no injunction in respect of the Community registered design in force anywhere in Europe."
It's supposed to remain there until 15 December. Pity they didn't stretch it through the Christmas period!

Monday, November 05, 2012

Mr Gove touting access to National Pupil Database

The Department for Education is holding a "Consultation on proposed amendments to individual pupil information prescribed persons regulations" a title, should it come to any notables' attention, likely to provoke a collective yawn.

Reading on down the consultation page, though, it is explained that this is
"A consultation on proposals to amend regulations to enable the Department for Education to share extracts of data held in the National Pupil Database for a wider range of purposes than currently possible.
The aim is to maximise the value of this rich dataset."
Seriously?

The current government really want to provide corporate and wider access to intimate details of school children's files? The NPD holds up to 400 variables on over half a million children including names, addresses, 'looked after status', 'in need status', birth dates, gender, ethnicity, first language, eligibility for free school meals, information about special educational needs (SEN), exam results, attendance, reasons for absence and exclusions. 

Here in full is what the Secretary of State for Education, Michael Gove told MPs this week:
"I am today launching a public consultation on proposals to amend the Education (Individual Pupil Information) (Prescribed Persons) (England) Regulations 2009 to enable the Department for Education to share extracts of data held in the National Pupil Database for a wider range of purposes than currently possible in order to maximise the value of this rich dataset.
The National Pupil Database holds one of the richest educational datasets in the world and forms a significant part of the education evidence base. It is a longitudinal database which holds information on children in schools in England. This includes pupil level data relating to school attended, teacher assessments, test and exam results by subject, prior attainment, progression and pupil characteristics.
We have already significantly expanded the content of school performance tables for primary and secondary schools and were commended in the National Audit Office report “Implementing Transparency” (April 2012) for opening up access to our data. Recently, we have also improved the application arrangements for requesting access to data from the National Pupil Database under our existing regulations for those who need pupil level data for research purposes.
However, we are aware that the existing Prescribed Persons Regulations may prevent some potentially beneficial uses of the data by third-party organisations, as use is currently restricted to “research into educational achievement”. For example, we have had to reject requests to use the data for analysis on sexual exploitation, the impact on the environment of school transport, and demographic modelling, all of which seem to be legitimate and fruitful areas for further research.
We want to give organisations greater freedom to use extracts of the data for wider purposes, while still ensuring its confidentiality and security. Existing arrangements for access to the data would apply to all future requests: all requests to access extracts of data would go through a robust approval process and successful organisations would be subject to strict terms and conditions covering their handling and use of the data, including having appropriate security arrangements in place. Organisations granted access would need to comply with the Data Protection Act, and any reports, statistical tables, or other products published or released, would need to fully protect the identity of individuals.
Amending these regulations should encourage more organisations to use the data for wider research, such as socio-economic analysis, or research into equality issues, including disability, gender or race. It could also help stimulate the market for innovative tools and services which present anonymised versions of the data.
If, having listened to the views expressed in the public consultation and subject to the will of the House, I decide to proceed with the proposed amendments, I expect the revised regulations to come into force in spring 2013.
The public consultation on this proposal will commence today and run for six weeks. A consultation document containing full details of this proposal and how interested parties can respond to the consultation will be published on the Department for Education website. Copies of that document will also be placed in the House Libraries."
Let's just pick out a couple of points from this.

Mr Gove wants "to give organisations greater freedom to use extracts of the data for wider purposes, while still ensuring its confidentiality and security." That will be a neat trick. I wonder if the Secretary of State has ever heard of diametrically opposed, mutually exclusive goals? Well whether he has or not he's found some here and he shouldn't need a Ross Anderson or a Bruce Schneier to explain why.

Next he says "Organisations granted access would need to comply with the Data Protection Act, and any reports, statistical tables, or other products published or released, would need to fully protect the identity of individuals... It could also help stimulate the market for innovative tools and services which present anonymised versions of the data."

Note that not even minimal effort is to be made by government to anonymise the data (imperfect though those methods undoubtedly are - anonymisation is really difficult) in advance of release. It is the organisations given access to the data who will have to pay lip service to "fully protecting [sic] the identity of individuals". And the private sector can beta test "tools and services which present anonymised versions of the data" on real live kids' personal details.

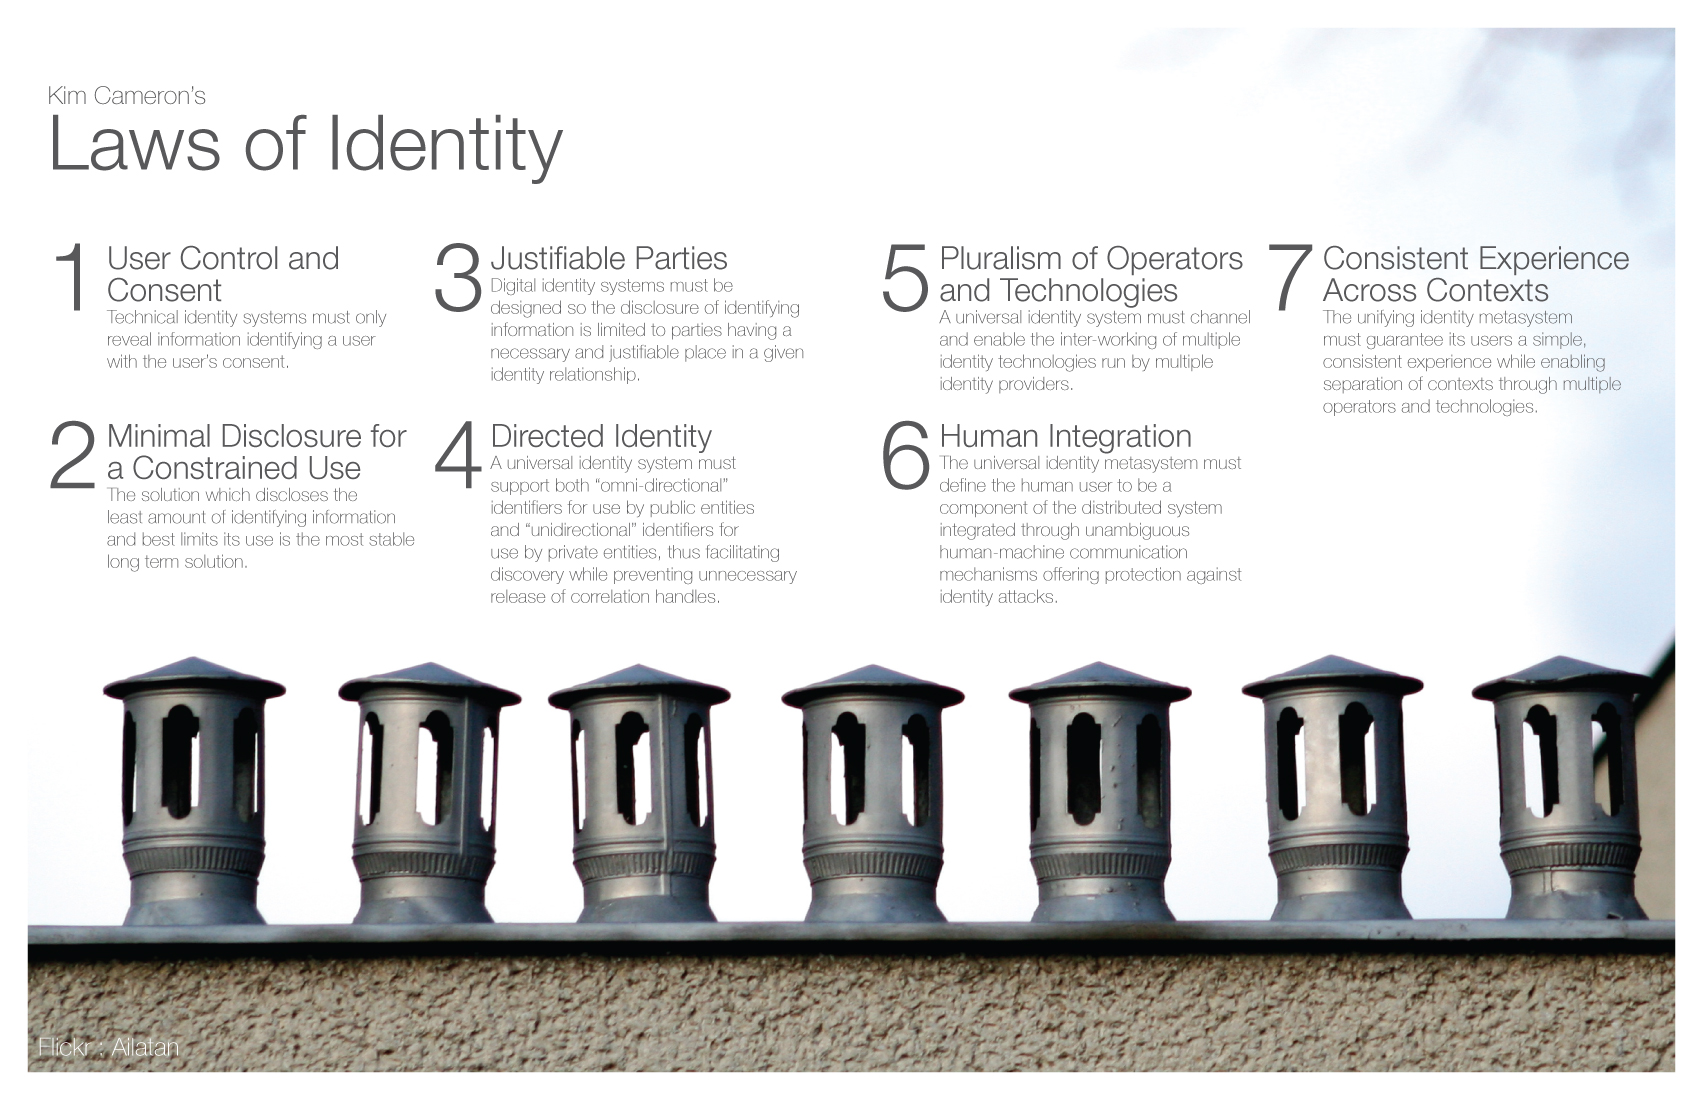
Just for starters, the whole thing breaches Kim Cameron's first three laws of identity.
1. User control and consent - technical identity systems must only reveal information identifying a user with the user's consent.
2. Minimum disclosure for constrained use - the solution that discloses the least amount of identifying information and best limits its use is the most stable long-term solution.
3. Justifiable parties - the information will be in control of or at least accessible by parties who have no right to it.
But then current government practice on facilitating access to this database already does that. The difference with this new proposal is one of scale and that's almost impossible to explain to a politician. If anyone has any bright ideas on breaking through this cognitive fog in a way that the average government minister would understand, answers on a postcard please or preferably in the comments below...

When Privacy International warned in the summer that the Department for Education sponsored an "appathon", allowing attendees access to the National Pupil Database I wasn't really too concerned despite their reasonable questions at the time:
"1) What data access arrangements will attendees be provided with?
2) What legal commitments will attendees be required to make?
3) What data protection/management guidance will be given to attendees?
3b) Given the use of an API, will synthetic data be provided for testing/debugging/public exhibition?
4) Who gave permission in the first instance and can we see the letter of agreement?"
Computer scientists have been warning, for decades, of the practical problems of securing valuable databases.  European and (to a lesser degree) the US courts have shown an inclination to step in to correct calculated or negligent mismanagement of or unauthorised access to such systems. The degree of such intervention by the courts would suggest they would look unkindly on untrammelled access to the NPD of the kind that Mr Gove appears to favour. But by the time that happens the damage would already be done.

Look, the enthusiasm for opening up government datasets is encouraging, when that doesn't compromise personal privacy. But transparency is not automatically always the right thing in all circumstances.

The problem of striking a balance between protecting privacy and facilitating empirical research/use of valuable datasets, like medical records or the NPD, in the public interest, is potentially one of the defining political issues of the 21st century. The technical and legal problems are also almost impossibly challenging, as FIPR, Paul Ohm and others have illustrated.

The NPD, however, is not the sandpit to be experimenting with all this.

Thursday, November 01, 2012

Debi Gliori, The Tobermory Cat & the angry artist

When my elder son was about six years old he picked up a novel with a hardback red, furry cover in a bookshop in Oxford, read the blurb on the back and said he's like me to buy it. Whereas I understood his attraction to the tactile cover (whichever Doubleday marketeer came up with that chalked up a successful capture in our case), once I'd read the back of the book and scanned the first chapter I didn't think he'd be interested in a gothic story, a seemingly Scottish Italian variation on the Addams family.

I was wrong.

He was captivated by the story, the characters, the sophisticated language, the black humour, the setting, the adventure and possibly most of all by the laptop of the geeky Titus Strega-Borgia.  A boy he projected to be close to his own age in possession of his own laptop. (Titus was 12 but it was close enough). That was something he could wield in his ongoing campaign to acquire an equivalent piece of kit for himself.

The book was Pure Dead Wicked by Debi Gliori, a book for older kids by an author better known for her picture books for younger children. Before we had finished reading it he had obtained the other two books in the 'Pure Dead' first series, Pure Dead Magic and Pure Dead Brilliant, having borrowed them from the library on multiple occasions before we actually got round to buying them.

Ms Gliori has now unfortunately found herself at the centre of a social media sparked/facilitated hate campaign, surrounding the publication of her latest book, The Tobermory Cat.

The managing director of Birlinn Books, Hugh Andrew, following a conversation with a bookseller in Tobermory about a local stray ginger cat, decided to ask first author Mairi Hedderwic, then Debi Gliori to write a book inspired by the cat.

Ms Gliori agreed.

Local artist, Angus Stewart, was not best pleased. He claimed to have made the cat famous by setting up a Facebook page about it and didn't like the notion of what he perceived to be a big powerful publisher and famous author cashing in on his idea. The local bookseller, Duncan Swinbanks, discovered Mr Stewart wasn't happy and set up a meeting.

The artist said they could do a book about a cat as long as it wasn't his cat. The publisher offered to advertise the artist's work on the back of the book. There was no meeting of minds.

The artist, Mr Stewart, made his feelings clear on his Facebook page and the angry mob took up his cause. Mob hatred and abuse directed at Ms Gliori, the publisher and his staff followed via phone and internet. Plus behaviour that might amount to at least defamation, possibly incitement, definitely a Communications Act section 127 and Public Order Act section 5 and Malicious Communications Act section 1 offence (though, like Lilian Edwards, I'm no fan of s127 or s5 or s1 for that matter), and maybe even stalking, though the latter might be a stretch. Mr Stewart, according to Ms Gliori, tracked her speaking engagements at libraries and contacted the librarians, just prior to her arrival, insinuating someone they knew was stealing his ideas. He apparently spread similar indirect and unsubstantiated hints of [non-existent] malfeasance by Ms Gliori through Twitter.

Debi Gliori outlines the dispute in her own words here.

The Facebook page on the Tobermory cat set up by Angus Stewart is here.

The publisher Hugh Andrew's reply to criticism on the Explore Mull site is here (scroll down to 'The Reply to the article above from the publishing company').

Mr Stewart tries to explain his stance in a writers' forum here. It doesn't appear as though he understands copyright or the trouble he might face if Ms Gliori decided to pursue criminal or defamation proceedings against him or his wrathful sympathisers. Young men have already been jailed, inappropriately in my opinion, this year for writing drunken hate and stupid grossly offensive messages through Twitter and Facebook.  I hope Ms Gliori or her publisher do not consider hiring lawyers to address this. Down that route lies the enrichment of lawyers and further distress for the author, artist and publisher.

But Mr Stewart needs to understand, wronged though he thinks he might be, that he has no cause for complaint, moral or legal, against Ms Gliori, her publisher or the bookseller. I'd recommend he peruse Thomas Jefferson's letter to Isaac McPherson or Macaulay's speeches on copyright to get a sense of perspective on what intellectual property privileges should be for.  For now I'll just quote an extract from Jefferson that I never tire of:
"It would be curious then, if an idea, the fugitive fermentation of an individual brain, could, of natural right, be claimed in exclusive and stable property. If nature has made any one thing less susceptible than all others of exclusive property, it is the action of the thinking power called an idea, which an individual may exclusively possess as long as he keeps it to himself; but the moment it is divulged, it forces itself into the possession of every one, and the receiver cannot dispossess himself of it. Its peculiar character, too, is that no one possesses the less, because every other possesses the whole of it. He who receives an idea from me, receives instruction himself without lessening mine; as he who lights his taper at mine, receives light without darkening me. That ideas should freely spread from one to another over the globe, for the moral and mutual instruction of man, and improvement of his condition, seems to have been peculiarly and benevolently designed by nature, when she made them, like fire, expansible over all space, without lessening their density in any point, and like the air in which we breathe, move, and have our physical being, incapable of confinement or exclusive appropriation."
Mr Stewart has on his Facebook page offered a link to Ms Gliori's perspective on the dispute. He should also act to mitigate the hatred and reputational damage he has unjustly unleashed by explaining clearly to his supporters, at least through his Facebook page, that offensive, indecent, obscene, menacing, threatening, abusive or insulting words or behaviour towards or about Ms Gliori and her associates are not acceptable.

I feel especially sorry for Ms Gliori since she has brought so much pleasure to my own kids and thousands of others. She may be well known but she is not independently wealthy -
"Let me just state for the record here : I do not have a trust fund. I have a heck of a lot of recipes for lentils. I have no back-up plan. These unknown persons were literally attempting to destroy my livelihood."
She does not deserve the anger and abuse. 

I'll leave the final word to the articulate Birlinn boss, Hugh Andrew -  
"Debi’s work is translated into some twenty languages and she is one of the finest children's illustrators and writers in the country. Birlinn is not some large corporate. It is an Edinburgh publisher founded by me that publishes books on or about Scotland and its communities. I have been visiting Mull to sell books three times a year for the last twenty years and we have published many books on the island, not all commercial. I do this because I love Mull and the West Highlands. These books are sent round the world and do not simply just generate revenue for the shops on the island.
We had therefore thought that a book publicising Mull, produced to the highest quality, written with love and affection and sold round the world would be welcome to the people of Mull, to those who visit the island, and to all who love the Highlands and Islands. And so it has proved to all bar one person. I deeply regret that Mr Stewart has chosen this path rather than working with us as we offered him the chance to do. I deeply regret that he is unable to see the damage he is doing to his own reputation by his obsessive campaign. I deeply regret his lack of understanding of laws of copyright, his inability to explain what it is he is claiming to protect. I deeply regret the portrayal of Mull he projects in his comments.
There is however a limited amount I can do about this. It is up to the people of Mull and visitors to vote. This autumn they will have a beautiful gift book on their island and on Tobermory. It will feature one of the islands better known residents, and he and his island will be taken round the world in a book that advertises the island. In the back of the book will be all the many Tobermory people and businesses to whom I owe so much of a debt over the years and who have given us so much help and support. It is a work completely independent of any other and a tribute to a beautiful place."

Tuesday, October 30, 2012

Stansted naked scanner images on public display

An old friend has been traversing Stansted airport and writes to say;
"Apparently if you set off the metal scanners you get to go and stand in the booth. So if you carry a small amount of change through the detector or you are unlucky enough to get picked at random (apparently that's why I ALWAYS set the alarm off) you get to be irradiated for your trouble. 
In the Stansted setup, the operator viewing the images sits alongside the other operators on the "secure" side of the checks and the full body images generated by the scanner are on full view to everyone who has already passed through security! 
So much for all the propaganda about the images only being seen by a single operator in a darkened room remote from the scanner eh?" 
The blatantly casual nature of this set up and the apparent lack of concern of the operators and the travelling public is just one further indicator of the unrestrained battering the ethos of personal privacy is taking in UK society. Sad.

By coincidence, for the first time in ages I had been speaking to another old friend on Friday who had recently been to Amsterdam.  He tells me that all passengers going through Schiphol Airport when he was there had to go through the strip search machine. No exceptions.

He thought it was great for two reasons. Firstly it seemed to him to speed up the queues - faster than the metal detector scan plus pat down. Secondly, since he's had a replacement hip he always makes the metal detector  beep, so he always gets a pat down.

The few studies that have been done of the effect of the scanners on queues indicate that on average they increase queuing times significantly, primarily because of the amount of time it takes to scan each individual. That reality is completely irrelevant, however, if people perceive the machines to be shortening queues. Convenience [perceived or real] beats everything, including a commitment to personal privacy.

In my Amsterdam friend's case he always sets off the metal detector and always gets a pat down, so the naked scanner felt far less intrusive and significantly more convenient.  He had not thought about the efficacy of the machines.  He just assumed that they work, whereas we know they don't detect some dangerous explosives.

He had not thought about what kinds of images were generated, whether they were legal, who saw them, when, whether and where they were stored, shared or further processed.

He had not thought about the health risks but assumed that element of the machines' deployment had been thoroughly reviewed, regulated, tested, certified and routinely audited, which of course is not the case.  He had no idea if the machine he went through was a millimetre wave machine - relatively safe from a radiation perspective as long as the machines don't malfunction as they are prone to do - or an xray backscatter machine - widely deployed at US airports and found by scientists at the University of California and elsewhere to pose significant health risks.

In short, he had no idea of or given any thought to the significant security, ethical, operational, legal and health & safety problems with the routine deployment of naked scanners in airports. And why should he - he had just had the most convenient, comfortable processing through airport security from his perspective for many years.

Cyber-rights folks - naked scanners have got to be the easiest, slammest dunkest, article 8 privacy breach to demonstrate to anyone.  If we can't convince intelligent folks what a terrible idea they are then Scott MacNealy, Mark Zuckerberg, Larry Page, Sergi Brin, odious Tony 'rights are an outdated 19th century concept' Blair and co are right - privacy really is well and truly dead.

A problem tidying links

I've done some housekeeping on the links in my sidebar, deleting previously useful ones that have been high-jacked by commercial enterprises and most that are no longer active.

I'm having a bit of a problem with the link to Jenny Levine's terrific Shifted Librarian blog. For reasons I can't fathom clicking on the link just bounces the browser back to B2fxxx. The Shifted Librarian blog is still going strong at theshiftedlibrarian.com.

I've used bog standard html to code it by hand into the links list.

I'm missing something obvious but what?

Tuesday, October 23, 2012

Virgin Media problem seems to be fixed

Well the chap from Virgin Media, Norm, arrived yesterday about 2pm with the new "Super Hub" to replace the old and ailing Ntl/Virgin modem and re-invigorate my home internet experience.

He'd had a pretty tortuous day himself up until that point with every job having unforeseen complications.  He had phoned me to say he was running late and in spite of the nightmare day, disgruntled customers, long hours of frustrating telephone tag with the office (it's not just the customers that get to play but the front line guys too), he retained a remarkably cheery disposition, that alone for which he should be commended. That he was prepared to do battle with his own organisation on behalf of their customers, whilst risking the wrath of those he was thereby delayed getting to, was doubly commendable.


We both joked we hoped that his fortunes were taking a turn for the better as he went through the process of connecting the hub.  He mentioned that the old type modem tended to go downhill fast and the hub should make an instant difference. We also had a fun back and forth about dysfunctional offices as the hub sprang into life.

I could disconnect the old Buffalo wireless router too since "Super Hub" does it all. It does mean of course that I'm going to have to retro-connect every wireless device in the house - all umpteen of 'em - to the new box but I guess that's the price of progress.

I had the laptop booted up and went through the process of connecting to the new box - disconnect from the old one, find the new one, connect, type in new password, wait... connected! Let's just check that - well it's a little slow but I can get on the Net.

The desktop was relatively slower but both were still better than what I've been seeing for the past week. By way of a bonus my outgoing Virgin account emails which were getting blocked with an error connecting to the outgoing server are now getting out again.

Norm toasted his first uneventful success of the day and I thanked him for his help and his efforts before seeing him on his way. He turned down the offer of a tea/coffee explaining that he was well watered at his previous jobs. Nice to know that despite their vexation his previous customers at least retained their courtesy and ensured he was kept hydrated.

I checked the broadband speed.  It was still relatively slow on the desktop - about 2.5Mbps - but much better on the laptop - over 20Mbps - pretty impressive by recent standards. Later in the afternoon the laptop was pulling download speeds in the 40+ Mbps bracket which is a huge improvement.  The PC got up to nearly 9Mbps

Having given it a day to settle in I checked the speeds again this morning.  The PC was still slow - 2.7Mbps at best. So I gave the browser a tune up and improved things drastically. Though the performance is still variable I'm getting download speeds this afternoon of up to 40Mbps though mostly low 30s. The laptop is running up to 43Mbps on download and up to 2.8Mbps on upload.

So thank you to Norm the star frontliner for fixing my recent internet connection woes. Thank you also to Dave and Marina at Virgin Media; the latter for picking up and orchestrating and efficient response to my note to Richard Branson and the former for diagnosing my problem and arranging the solution.

My son tells me there seems to be a problem with the Xbox, so we'll have to monitor that. I haven't reconnected all the wireless devices yet so we'll have to see how that goes too.  But on the basics - robust higher speed internet connection - things appear now to be fine compared to this time last week. A day in I'm now running relatively seamlessly. Let's hope it stays that way.

A final note for Mr Branson.  Although you probably remain unaware of my problems, thank you too for employing smart and caring staff, Marina, Dave and Norm. On this occasion I had the good fortune to have my difficulties come to their attention and once a problem is in the hands of good people, it's well on the way to getting fixed.

Monday, October 22, 2012

CDB: Snoopers' charter or improving security

Index on Censorship ran a session on the Communications Data Bill on Thursday last, 18 October. Home Office Minister Jeremy Browne was originally slated to appear but the Home Office decided in the end they could not offer anyone. John Kampfner chaired the panel featuring Emma Ascroft (Director, Public Policy, Yahoo! Europe), Jamie Bartlett of Demos, Dr Ian Brown (Associate Director, Cyber Security Centre, and Senior Research Fellow, Oxford Internet Institute) and Kirsty Hughes (Chief Executive, Index on Censorship).

John Kampfner opened by saying the Home Office had unfortunately not had anyone available and thanked Jamie Bartlett for stepping into the fray at the last minute to offer a "mild version" of their perspective. He then invited Ian Brown to open proceedings, later disclosing he had briefed Ian to stick to as balanced and factual a serving as possible.

Dr Ian Brown. OII.

Ian started with a quote from Security Minister, James Brokenshire, in Thursday's Guardian, defending the communications data bill and arguing that terrorists are using internet messaging, phone services and video games to communicate, so the government needed to track it all.  Ian agreed that the first job of government was to look after the security of citizens and that there is a non trivial threat from terrorism to the UK that even the most ardent civil rights campaigners would not deny.

There is already a legal requirement for ISPs and phone companies to retain data. The Home Office say terrorists know this and as a result are moving to social networks, games etc and therefore they need access to that data too.

In reality they are wanting to take a narrow power and broadening it to any person who controls or supplies a communications service, a communications service provider (CSP). The Secretary of State can make changes by order.  The CDB also allows government to say they are not building a giant central database since it is the ISPs and other technology companies that will be holding the data.

Ian said there were two key issues:
  • Firstly the rhetoric from government is that this is "all about terrorism".  But if you want to tackle/prevent terrorism mass surveillance is useless compared to targeted surveillance. Government believes the hype from tech vendors of surveillance kit that all they have to do to stop the next 9/11 is gather all the data on everyone and mine it.  Unfortunately the technology is no where near doing the kinds of things that are claimed for it. The US government know this from an officially commissioned scientific report published earlier this year. So anti-terrorism is a red herring.
  • Secondly the data collected under the CDB will be used for all kinds of purposes which have nothing to do with serious crime. You only have to look at the abuse of data collecting under the Regulation of Investigatory Powers Act to see this.  The CDB will very seriously infringe on EU privacy rights. These privacy rights are not absolute and if the government has serious social, national security or economic reasons for overriding them they are entitled to do so. But there are indications from high courts around Europe and from the European Court of Human Rights that the kinds of invasions that would be facilitated by the CDB would eventually be declared unlawful.  The Bulgarian and Romanian supreme courts have disapproved of data retention. The Irish High Court has declared it important to limit and control data retention and has referred the issue to the European Court of Justice. Ian didn't quote him but it's worth pointing out what Mr. Justice McKechnie said in that case:
"Given the rapid advance of current technology it is of great importance to define the legitimate legal limits of modern surveillance techniques used by governments… without sufficient legal safeguards the potential for abuse and unwarranted invasion of privacy is obvious… That is not to say that this is the case here, but the potential is in my opinion so great that a greater scrutiny of the proposed legislation is certainly merited."
In addition to courts in Ireland, Bulgaria and Romania, the European Court of Human Rights has examined these issues quite closely in the case of S & Marper v UK, relating to the unlawful retention of DNA and fingerprints of innocent people.  There are more than 5 million people on the UK DNA  police database. That is now being changed, in theory, under the Protection of Freedoms Act, as a result of the S & Marper decision.

In the S & Marper case the UK government trotted out all the old worn arguments about why they needed blanket data collection - e.g. collecting the data doesn't infringe anyone's privacy; only using it would infringe privacy - and a whole host of others. The Court completely rejected this line idea and all the others.  Of course the blanket retention of fingerprints and DNA of innocent people infringes their privacy.

Ian recommends everyone should read the S &Marper judgement. In his opinion it comprehensively deconstructs and rejects all the excuses trotted out to justify blanket data retention. I agree it is worth reading. If you can't face the full judgment, I did a blog post on the key extracts at the time. The ECHR came as close as it could, without saying so directly, to accusing the UK government of lying about the statistics they used to "prove" how good mass (fingerprint and DNA) data retention would be for serious crime detection and prevention.

The S & Marper decision is a clear indicator that, should the CDB be passed in its current form, the European Court of Human Rights would eventually declare it incompatible with the European Convention on Human Rights. Unfortunately there would be significant damage done to our society and our system of justice in the many years it would take for this to happen.

John Kampfner then invited Emma Ascroft from Yahoo! to provide the company's perspective.

Emma Ascroft. Yahoo!

Ms Ascroft opened by saying that Yahoo1 is a member of the Global Network Initiative (GNI) and by quoting Liberty who have criticised the CDB as "massively enabling and lacking in prescriptive detail". She recommends the Liberty written submission to the Joint Select Committee on the draft CDB as a good summary of the primary concerns.  Liberty's submission starts at page 254 of the so far published written evidence. My own submission and quite a lot of others were omitted from this publication as a result of an error, due, I am told, to be put right shortly, now the latest set of oral evidence hearings have been completed last week. You can get a sense of Liberty's stance from their opening paragraph:
"It is no exaggeration to say that these legislative proposals signal a major shift in the relationship between the communications industry, the state and the public. Never before have private companies been called upon to orchestrate blanket collection of personal data which they have no business reason to retain."
Ms Ascroft then went on to say that the CDB could be relatively benign - just a tidying up of the loose ends of the Regulation of Investigatory Powers Act. (I noticed Kirsty Hughes stiffen visibly at this point, at the implied notion that RIPA was itself relatively benign). However it could also be hugely intrusive. The Home Office is sitting somewhere on the spectrum in between the two, she believes.

Section 1 of the bill means there would be no further parliamentary scrutiny once the Bill became law.  The Home Office continually tells us not to worry and just take the details on trust.

Yahoo! think the CDB would give governments in the 57 different jurisdictions they operate in the green light to adopt similar laws. It would be a dangerous tool for repressive regimes.

There are more proportionate approaches to tackling the use of networks for nefarious ends.  For example the use of bilateral Mutual Legal Assistance Treaties (MLATs). These respect the fact of jurisdiction limits rather than extending government powers to access personal data into other sovereign jurisdictions.

On whether the CDB is a snoopers' charter Ms Ascroft agreed that safeguarding security was the duty of government.  RIPA is 12 years old now and needs reviewing.  Yahoo! are very concerned about the way the RIPA review happened.  There was no public confidence in the process through which RIPA came to be reviewed.  When considering these kinds of laws we need an inclusive, consultative, evidence based and transparent process. The process in relation to the CDB has been anything but transparent.  The Home Office says the world has moved on and the government has access to 25% less data for tackling serious crime.   But they refuse to disclose what they mean by that 25%.  In Australia there is a much more open process around the development of internet crime laws.

Civil society and the Global Network Initiative (GNI) are pushing for transparency. The CDB is pushing in the opposite direction.  CDB orders would be served on companies without public scrutiny.

Kirsty Hughes. Index on Censorship.

Kirsty Hughes of Index on Censorship was next to the party. She opened by saying she agreed with a lot of what had been said in criticising the Bill but also fundamentally disagreed with the notion that the first duty of government was security. 

She wanted to remind us of fundamental principles. The first duty of government was the protection of liberty.  Index say the CDB would be a snoopers' charter. It will be the most intrusive form of surveillance anywhere and will be widely imitated.

Foreign Secretary, William Hague goes round the world saying we like free speech and it's important to protect the rights of people.  The Home Office does the opposite.

The CDB is about privacy and free speech.  A lot of critical discussion is focused on privacy alone but they go hand in hand.  This is not just about the digital world. Look at the history of detailed Stasi surveillance and the chilling effect of that.  An Azerbaijan citizen recently told her he has to live his life as if he is constantly in public since he doesn't know exactly when he is being tracked/watched and when not.

Again she emphasised government's first duty is to protect rights. Then at the margins they need to look after security. Having an open, democratic, rights based society is inherently secure.  There is a fundamental question about the direction of travel.

The extent of the CDB proposals in facilitating the collection of population wide data is completely disproportionate and indicative of a police state.

There are lots of questions on what constitutes traffic and what is content data and whether the two are clearly distinguishable. (I highly recommend Peter Sommer's submission to the Joint Select Committee starting at page 412 to get an in-depth understanding of the issues here). The range of data that is now available can give an extraordinary picture of people's lives.

The CDB risks undermining anonymity and therefore whistle-blowing. The chilling effect is huge.

We have seen it already on other systems where personal data is collected and passed on to less savoury regimes.

The fact that you can do something technologically does not mean you should do it. It's bad civic hygiene to deploy such systems because of the damage they do to our democracy, our rights, our society and our security.

Jamie Bartlett, Demos.

The final member of the panel to speak was Jamie Barlett, Demos Head of the Violence and Extremism Programme, and Director of the Centre for the Analysis of Social Media. Mr Bartlett was joint author of the Demos paper #Intelligence published earlier this year which argued that social media should be used for intelligence purposes. Hence John Kampfner's characterisation of his perspective as a mild version of that of the Home Office.

Mr Bartlett opened by saying he is mildly in favour of the extension of general surveillance to social media. He think the CDB does not go far enough and believes it has been unfairly misrepresented as a snoopers' charter through which the UK will join repressive regimes like Iran, China etc in using deep packet inspection to spy on citizens.

Mr Bartlett believes there is a world of difference between states that pass laws like the UK in a democracy and those that pass laws without public consent like Iran. Democratic states all do snooping, surveillance, bugging etc but it is regulated. And there are other states with similar provisions to the CDB.

Is the CDB an extension of powers? He does not think so. This is about comms and traffic data that the government already collects routinely. (Only two minutes in that's the biggest of a series of misstatements).

There are lots of reasons the government need access to comms/traffic data.  The Home Office believes there is an increasing degradation in the data it has. Under the CDB they will still have to go through the same process to get access to the data as through RIPA. (I'm beginning to suspect that Ian Brown may point, in rebuttal if given the opportunity, to some holes in this perspective.  The CDB, vague though it is, will significantly change the process of getting access to data).

Mr Bartlett agrees with the other panellists about the vagueness of the detail in the Bill and has a clear problem with this.  We need a public debate on what data should be collected and how etc.

His second major problem with the Bill in its current form is the degree of oversight the processes of collecting and accessing the data will receive. This is not clear.

There are also already too many agencies getting access to data under RIPA. We should take a narrow approach as to which agencies need access under the CDB. RIPA is based on a sliding scale - the greater the intrusion allowed, the fewer agencies can do and for fewer purposes. (I'm not sure that's entirely representative of RIPA processes.)  Access to comms data (e.g. browser history) can be more intrusive than access to traffic data.  He'd like a sliding scale like RIPA.

The concern that most people have is that the agencies of state can easily and routinely collect and traverse this data for their own purposes.  This is being done already and not just by the state. Commercial enterprises are doing it on an industrial scale and the scale of what the FBI is doing is staggering.

Currently directed surveillance by a police officer of someone on a public highway - e.g. following a suspect in a public place - can be done with a minimum of authorisation or oversight. Online state, private or commercial actors can do much more than this directed surveillance now. And it is being done with no control at all.  It has to be regulated.  Hopefully the CDB will go some way to getting this activity under control.

Q&A

John Kampfner then directed three questions at Jamie Bartlett.

Firstly did Mr Barlett believe the CDB was legislation based on consent and he alluded to a Sunday Times exposé about government making laws in dark smoky rooms.

The second question was whether he believed the Bill dealt in the voluntary handing over of data by communications service providers.  It seemed to Mr Kampfner that there was nothing voluntary about the draft provisions.

Thirdly he asked did Mr Bartlett have evidence of other democracies that have similar laws to the proposed CDB.

Jamie Bartlett said firstly he was not in favour of any secret surveillance powers that were not based on legislation.

Kirsty Hughes of Index interrupted with a question, asking if Mr Bartlett believed that a majority in Parliament had the right to turn us into a police state, overriding her human rights.

Ian Brown pitched in by agreeing that one of the fundamentals of human rights was that the majority cannot override the rights of minorities.

Jamie Barlett said he has significant concerns about the lack of clarity of the CDB.

John Kampfner then directed the question about the voluntary nature or otherwise of the handing over of data at Emma Ascroft of Yahoo!

Ms Ascroft said UK companies have an obligation to retain data for 12 months under the data retention regulations.  The CDB would extend this to new data types.

There would be a second obligation to generate data types specified under order. As far as non UK providers are concerned that constitutes an attempt by the UK to extend its jurisdiction beyond its borders. There is a significant question about whether the government can do that.

It would be better to use MLATs (mutual legal assistance treaties).  This would be more proportionate.  Law enforcement authorities find the MLAT process slow.  But as far as Yahoo! are concerned the communications providers are not the ones holding up the process.  The CSPs are not on the critical path and it is the government to government processes that are causing it to be slow.

The Home Office has never had a sensible policy discussion around MLATs.

Jamie Barlett came back in at this stage to answer Mr Kampfner's third question.  Other democracies, he said, have not passed into law powers as extensive as those in the CDB.  But they have worse right abusing laws in other contexts. He started to use an example from France when John Kampfner interrupted asking he address the question of similar provisions in other democracies to the CDB.

Mr Bartlett said ok.  The UK is the biggest terror target in Europe.  He accepts other democracies don't have CDB equivalents.  But we need regulated, transparent and clear surveillance powers.

John Kampfner said he had been in Russia recently and the Russian authorities were taking great cheer from the UK introducing these kinds of laws and using them to justify their own surveillance laws. They will be happy to bounce the UK's own repressive regulations back at them in response every time the UK government dares to lecture them hypocritically about their human rights abuses.

Mr Bartlett said we have to understand we are doing this data collection and access already. So it needs to be properly regulated.  Companies already given government 75% of the data they want anyway.

John Kampfner moved on.  Tony Blair post 9/11 said "the rules of the game have changed... do whatever it takes".  Mr Kampfner then asked Ian Brown whether the potential monitoring of millions is ok if you stop one terrorist outrage.

Ian responded that you can make that argument about any democracy.  Blair also said "human rights are a terribly outdated 19th century approach." Security is important but not at the price of breaking our democracy. The price of freedom is eternal vigilance.

Kirsty Hughes said the lack of judicial oversight in the CDB is a huge problem. And in spite of the benign perspective hitherto given on RIPA it is a terrible act in many ways and a poor starting point for further legislation in this area.

Emma Ascroft said a big change under the CDB would be to broaden the range of providers to include social networks, domain name registries and anything that might remotely touch on telecommunications.

The consequences for commerce, if other jurisdictions follow suit with their own brand of CDBs, will be to be faced with a complex international portfolio of national laws, with private companies potentially becoming the arbiters of what is allowable and what not, in relation to data collection and access.

With RIPA there was a big public consultation. Even after 9/11 there was a big consultation with companies prior to the passing of the Anti Terrorism Crime and Security Act 2003. But in the case of the CDB there has been no consultation. The debate has not happened.

For lawful access to data it would be better for the CSPs if government authorities used the MLATs.  The Home Office says it has no intention to undermine MLATs but the CDB.

Kirsty Hughes said this is not about a clear and neutral security threat.  The CDB is that latest in a long line post 9/11, 7/7, 11/3, liberty destroying laws. Absolute rights have been compromised and even torture approved, sold on the populist message of the need for blanket surveillance.

Jamie Barlett thinks the CDB should be withdrawn and replaced with a green paper and proper public consultation going forward.

Emma Ascroft said the CDB provides and extension of jurisdiction and a backstop power - when a provider refuses to collect and provide extra jurisdictional data - to enable a third party agency through deep packet inspection or other alternative process, to collect the data, even without the knowledge of the primary provider. That is indefensible.

At this point the Chair opened questions to the audience.

Paul Bernal of UEA was first.  He pointed out that politicians simply do not understand what they are dealing with when attempting to draw up regulations for modern technology. That is a serious fault line in our law making process.

Emma Ascroft agreed that the Joint Committee is "on a steep learning curve".  Parliamentary ability to scrutinise proposals depends on understanding of the technology and having enough detail in the Bill to scrutinise.  The committee, she is confident, has some good advisers.

Ian Brown agreed too that most parliamentarians do not have a technological background.

Anna Fielder from Privacy International  asked if anyone on the panel had compared the CDB to the USA/PATRIOT Act.

Emma Ascroft said the US doesn't apply data retention in the same way as the EU.  They rely much more on "data preservation". Law enforcement contact the communications provider and say they have identified a suspect and ask the provider to collect and retain the data on that suspect.  There is a fundamental difference of principle here - targeted as opposed to mass surveillance.

The Home Office did not even consult the Ministry of Justice or other government departments before going ahead with the CDB.  It is by no means clear that the Bill attracts whole government support.  The Home Office declared after 9/11 that they were unilaterally introducing data retention.  The Information Commissioner at the time told them they could not force ISPs to retain data that data protection law required them to destroy.

If you have 12 months data retention and extend that extra territorially then you can expect other countries to follow suit.  Therefore UK citizens' data will be available to other jurisdictions on an extra territorial basis.

Ian Brown said we cannot keep these massive valuable data silos secure. He also mentioned the example of Chinese hackers getting at the Google accounts of human rights activists as well as Google's proprietary source code, the release of which could do Google significant commercial damage.

John Kampfner then invited the panellists to close.

Ian Brown hopes that the Lib Dem branch of the coalition government will force the CDB to be withdrawn and force the Home Office to consult more widely. The more proportionate approach on digital network surveillance is to go through MLATs. The UK should be setting an example to avoid a race to the bottom on surveillance grabs.

Jamie Barlett, a bit bruised, said he agreed with a lot of the points made by the other panellists especially about the process surrounding the CDB.  He is impressed with the Joint Select Committee who have been critical of both the process and the Bill.  The question he says we need to ask is whether in 10 year the police and the Crown Prosecution Service will have the data to do their jobs. If they only have access to 10% of the comms and traffic data they need we will be in trouble.  But more generally, access to social networking and media content needs to be regulated better.

Emma Ascroft concluded by admonishing the Home Office for claiming communications service providers supported the CDB.  That was a big claim when they had not involved the companies in the process.  John Kampfner interrupted to ask was the Home Office, then, telling a porky pie?  Emma Ascroft suggested it might be better to suggest they were being economical with the truth.

We need engagement but with more detail so we can figure out and debate the detail.  The department of Justice, the Culture department and other parts of government really don't approve of the CDB.  The Home Office are trying to drive it through when the range and depth of stakeholders is huge.

What would be an acceptable outcome for CSPs?  CSPs do not want to be asked to catch and retain third party data. This is not proportionate. For non UK providers there are other mechanisms such as the MLATs. It is also not acceptable for CSPs to have 3rd parties hacking, mining, retaining and passing on their data through surreptitious means.

Kirsty Hughes rounded off.  The CDB is a sledgehammer to crack a nut. There is a serious risk that even if it gets amended it will not get amended enough. We need the voice of the UK out there defending digital freedoms not undermining them. Just think about the criminalisation of speech on social media.  The CDB is worse than anything that has come before in this area.  It is not just a slippery slope.  It is a drop to the bottom of the barrel.

Friday, October 19, 2012

Accidental redesign

By accident I messed up the B2fxxx template on blogger and then got drawn into playing with the new style features.  I'm not sure I like it but I've already wasted too much time I don't have this evening, so I'll leave it for now unless informed it's unusable. Now to get back to that Communications Data Bill article... before security lock me into the building...

Wednesday, October 17, 2012

Dear Mr Branson... about that poor broadband service

I've written to Richard Branson at richard.branson@fly.virgin.com to point out I'm less than enamoured with the poor service I've been getting from Virgin Media.

Dear Mr Branson,

Your Virgin Media broadband service which I subscribe to at home has been variable for several weeks.  The past three days it has become virtually unusable with download speeds alone slipping below 0.1Mbps. Typically it might run at about 1Mbps if we’re lucky though it did at one point reach 2 Mbps after 9pm last night.

This is disrupting my family’s work, education, social activities and access to public and commercial services.

Your “check service status” facility on the web – which I can only now check easily from my computer at work –


laughably says there is “Good service” in my area.

Your “check service status” phone line “confirms” that Virgin Media believe/assert “there are no problems” in my area.

When there are problems it is really irritating for customers when Virgin Media declare/think/pretend there are none.

The do-it-yourself (DIY) ‘check and fix your own problems’ approach on the Virgin Media website assumes customers have nothing better to do than follow a series of instructions which rarely fix anything and generates significant angst.

Your various “helplines” – which request a customer “press 1 for…” queuing,  canned music and repeated “your custom is really important to us”, “our lines are currently very busy and you may have to wait up to 25 minutes to speak to an operator” message privileges, then eventually at the end of a long wait connect to a stressed member of call centre staff in Asia who can’t help, is working to an instruction sheet not related to my problem and is occasionally just plain rude – are not conducive to already fragile customer relations.

As an academic in the area I know a little about computers – not a lot but a little – and one of my least favourite activities frankly, when I get home from work, is going through a series of convoluted, difficult to access (via your website or phone helplines) routine processes I know to be futile, in an effort to demonstrate to one of your difficult to access call centre folks that I’ve already tried the stuff on their crib sheet without success.

As to the website can I request that you yourself try the “Contact us” area of your website:

contact.virginmedia.com/

Click on that “Fault with your service” button.

Do you know if you have ‘cable’, ‘national’ or other options services?

Try ‘cable’ for the sake of argument.

Oh look it’s got that “check your service status” in your area button.  Ignore that – I can tell you it gives a false answer.

Instead “Select an option or search to see our top answers.”

Try “Cable broadband/wireless”.

Here we go there are “4 possible results to your query found”, in red font so this intrepid website miner can find them.

Click on “Why is my connection slower than usual?”

Great, an article on why my connection might be slower than usual with lots of DIY instructions, links to yet more articles and lists of instructions about rebooting my modem and optimising my computer or browser and Uncle Tom Cobley and all.  It even gives me the option at the end of every page of clicking a button
Was this information useful? Yes No

Guess what? 

The answer is no.

I know you’re a busy man and so am I, so can I just, as our US friends like to say, cut to the chase?

When there is a problem with my broadband service – it’s slow and/or down – I want Virgin Media to know about it and let me know about it in an accessible communiquĂ© whilst assuring me they are working hard to fix it asap. 

Then I want them to work hard to fix it asap and deliver the service I’m paying for.

If Virgin Media are traffic managing my service I want them to let me know about it immediately and why.  I don’t want to go Virgin Media website mining or trying to interpret tables or articles or links or messages or help forums or other places I might get directed to.  We don’t use “Napster, Kazaa, iMesh, eMule and so on” so should not be subject to traffic management. But if your people think we do I want to know about it.

Pretending there is no problem and then acting as though, if there is, it is all my fault doesn’t sit well with my perception of your preference for the delivery excellent customer service.

I’ve been flooded with letters from BT for months, encouraging me to switch to BT infinity.  Recent experience with Virgin Media (and I haven’t even mentioned the heavy static on the phone line because that’s another long story) is pushing me in their direction.

If you have, thanks for taking the time to read to this to the end.

Yours sincerely,

Ray Corrigan
I got a canned response:
"Hello

Many thanks for your mail to my airline office.

As much as I'd like to respond to everyone personally, it's not always possible.  If you're giving me some feedback about a recent Virgin Atlantic flight I'll make sure it gets to the right people.

If you are letting me know about one of my other companies, I'm always pleased to receive the feedback. However to avoid any delay in getting back to you can you please check www.virgin.com for a list of the other Virgin Group companies and get in touch through the 'Contact Us' section of their websites.

Best regards
Richard"
The "Contact Us" section of your websites is one of the fundamental problems but I have now heard from the 'Ceo team'.  So we'll see if that leads to a solution.

Update: I've now heard from a Virgin CEO complaints manager and a specialist agent.  The agent, Dave, who was very helpful and professional, has remotely diagnosed the problem as my troublesome old Virgin modem and is sending someone out to install a new one next Monday. I also agreed to sign up for a 60M service for £6.70 less per month than the current 10M service. Hopefully that will cure the problem as well as providing a better (faster/seamless) broadband service (and not create any other problems). It means committing to Virgin for another 12 months but that's ok as long as the service is good. Thanks to the individuals at Virgin who have been so helpful so far.  It beats playing telephone tag and website miner for days on end without respite.